Last tested: November 9, 2026 · By Alex
NET::ERR_CERT_AUTHORITY_INVALID is Chrome’s way of saying it could not build a path from the site’s certificate to a root certificate it trusts. The certificate may be perfectly valid for the domain and not expired, yet Chrome cannot verify who issued it, so it stops the connection with “Your connection is not private”.
On a public website this almost always comes down to the server: a missing intermediate certificate, a self-signed or default certificate, a test certificate, or a Cloudflare Origin CA certificate that visitors reach directly. On internal sites and local development it usually means the private CA is not installed on the device.
This guide focuses on the Chrome-specific chain problem and shows how to check it with openssl s_client, curl and SSL Labs. If the same warning appears in every browser, or only on a company network or with antivirus HTTPS scanning, start with SSL Certificate Not Trusted, which covers interception and trust store issues in depth.
Quick Fix
If you run the website:
- Run
openssl s_client -connect example.com:443 -servername example.comand read theVerify return code. - Point the server at
fullchain.pem(leaf plus intermediates), notcert.pem. - Replace self-signed, default or Let’s Encrypt staging certificates with a trusted one.
- If you use a Cloudflare Origin CA certificate, keep the DNS record proxied or switch to a publicly trusted certificate.
- Reload the web server and re-test from outside your network.
If you are a visitor: open the site on another device or network. A failure on every device means the server must be fixed; a failure on one device points to the visitor checks further down.
What NET::ERR_CERT_AUTHORITY_INVALID Actually Means
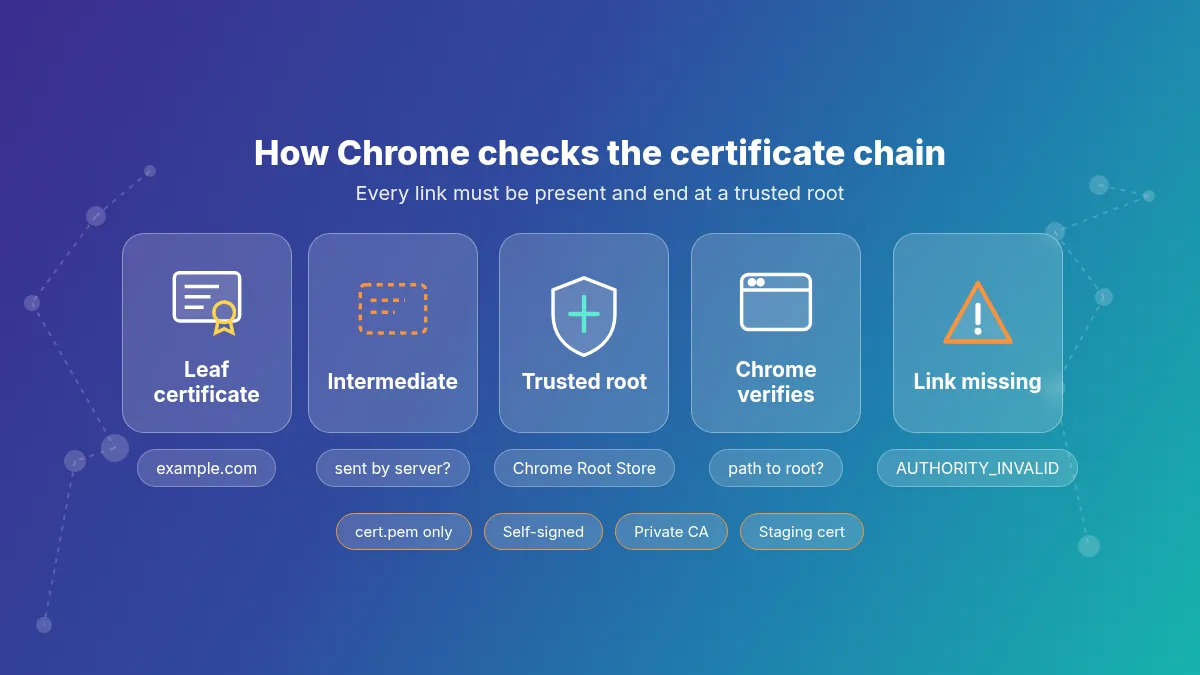
Every HTTPS certificate is signed by an issuer. Chrome checks the chain link by link:
- Leaf certificate – issued for your domain and sent by your server.
- Intermediate certificate(s) – issued by the CA and also expected from your server.
- Root certificate – already stored on the device; Chrome uses the Chrome Root Store on most platforms, plus roots an administrator adds to the operating system.
If any link is missing, or the chain ends at a root the device does not have, Chrome reports NET::ERR_CERT_AUTHORITY_INVALID. It is a trust-path failure, not a server crash and not a performance problem.
Two problems people often blame are actually different errors in Chrome. An expired certificate gives NET::ERR_CERT_DATE_INVALID, and a certificate for the wrong hostname gives ERR_CERT_COMMON_NAME_INVALID. If you see AUTHORITY_INVALID, focus on the issuer and the chain.
How It Differs From Similar Certificate Errors
| Error | Where you see it | Usual cause |
|---|---|---|
| NET::ERR_CERT_AUTHORITY_INVALID | Chrome, Edge, other Chromium browsers | Incomplete chain, self-signed, private or test CA |
| SSL Certificate Not Trusted | Any browser or app | Broad trust failure, often interception or old trust store |
| SEC_ERROR_UNKNOWN_ISSUER | Firefox | Same chain problem, checked against Firefox’s own store |
| NET::ERR_CERT_DATE_INVALID | Chrome | Expired certificate or wrong device clock |
| ERR_CERT_COMMON_NAME_INVALID | Chrome | Certificate does not cover the hostname |
| Cloudflare Error 526 | Cloudflare error page | Origin certificate invalid in Full (strict) mode |
Firefox users get SEC_ERROR_UNKNOWN_ISSUER for the same broken chain, and Cloudflare-proxied sites show Error 526 when the origin certificate fails validation.
Why This Error Happens
1. Missing Intermediate Certificate
The most common production mistake. The server sends only the leaf certificate, for example because Nginx points at Let’s Encrypt’s cert.pem instead of fullchain.pem, or the CA bundle field in the hosting panel was left empty. Some clients can download a missing intermediate on their own or already have it cached, so the site may look fine on your laptop and fail on another device, in curl or in an app. Do not rely on that: serve the full chain.
2. Self-Signed or Default Certificate
A self-signed certificate is its own issuer, so there is no CA to trust. You often get one by accident: Apache’s default ssl-cert-snakeoil.pem, a control panel’s placeholder certificate, or a reverse proxy such as Traefik serving its built-in default certificate when automatic issuance failed.
3. Private or Internal CA
Company intranets, NAS boxes, routers and staging servers often use certificates from an internal CA. They are valid only on devices where that CA’s root has been installed.
4. Test or Staging Certificates
Let’s Encrypt’s staging environment issues certificates from a test CA with “(STAGING)” in the issuer name. They are meant for testing automation and are not trusted by browsers. The same goes for certificates generated by local tools for development.
5. Cloudflare Origin CA Certificate Seen Directly
Browsers do not include Cloudflare’s Origin CA; only Cloudflare’s edge accepts those certificates. Everything is fine while traffic goes through the proxy (orange cloud). Once a record is set to DNS only, a subdomain is not proxied, or someone opens the origin IP directly, visitors receive the origin certificate and Chrome shows this error.
6. Wrong Certificate Served (SNI)
On a server with several sites, a request that does not match any virtual host falls through to the default one, which may carry a self-signed or unrelated certificate. This happens after adding a new domain, or when listen 443 ssl blocks are missing for www.
7. Interception or an Outdated Device
Antivirus HTTPS scanning, corporate proxies and very old operating systems can also break the chain on the visitor side. That is covered in SSL Certificate Not Trusted and Your Connection Is Not Private.
How to Check the Certificate Chain
In Chrome
On the warning page click Not secure in the address bar, then Certificate is not valid. In the viewer open the Details tab and look at the Certificate Hierarchy. A single entry means the server sent only the leaf or the certificate is self-signed. Check the issuer name for “STAGING”, “Origin”, “snakeoil” or your company name.
With openssl s_client
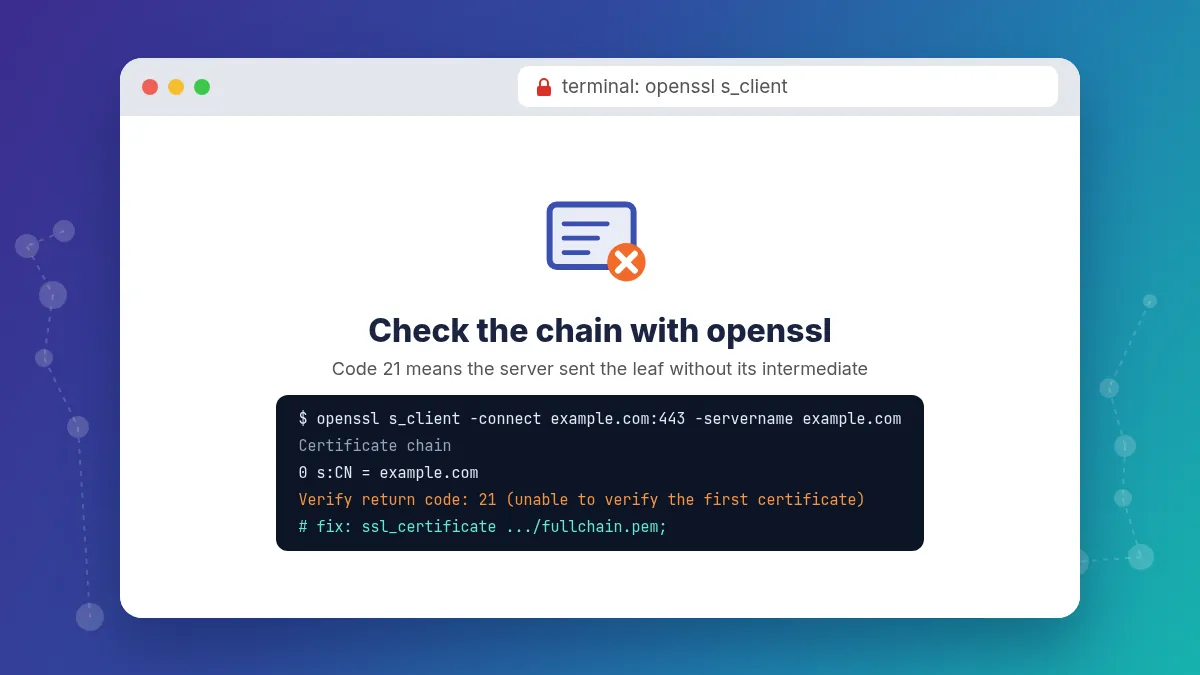
Replace example.com with your domain. The -servername option sends SNI, so you test the same certificate a browser receives:
openssl s_client -connect example.com:443 -servername example.com -showcerts </dev/null

# Issuer, subject and dates of the leaf only:
echo | openssl s_client -connect example.com:443 -servername example.com 2>/dev/null \
  | openssl x509 -noout -issuer -subject -dates

# How many certificates does the server send? (2 or more is normal)
echo | openssl s_client -connect example.com:443 -servername example.com -showcerts 2>/dev/null \
  | grep -c "BEGIN CERTIFICATE"
Read the Verify return code line near the end of the output:
| Return code | Meaning | Typical fix |
|---|---|---|
0 (ok) | Chain verifies against the local trust store | Server chain is fine; look at the client side |
20 unable to get local issuer certificate | Issuer not found: intermediate missing or root unknown | Serve fullchain; install private root on clients |
21 unable to verify the first certificate | Server sent the leaf without its intermediate | Use fullchain.pem or add the CA bundle |
18 self-signed certificate | Leaf is self-signed | Install a CA-issued certificate |
19 self-signed certificate in certificate chain | Chain ends at an untrusted root, often a private CA | Install that root on clients or use a public CA |
The openssl trust store is not identical to Chrome’s, but for public sites the results match closely enough to diagnose a broken chain.
With curl
curl -vI https://example.com/ 2>&1 | grep -iE "issuer|subject|SSL certificate problem"SSL certificate problem: unable to get local issuer certificate is curl’s version of the same failure.
With SSL Labs
Run the free SSL Server Test from Qualys SSL Labs (ssllabs.com/ssltest). In the report, Chain issues: Incomplete and an Extra download label in the certification paths mean an intermediate is missing. The test checks from outside your network, so it also catches cases where only your own machine has the intermediate cached.
Fixing NET::ERR_CERT_AUTHORITY_INVALID (Website Owner)
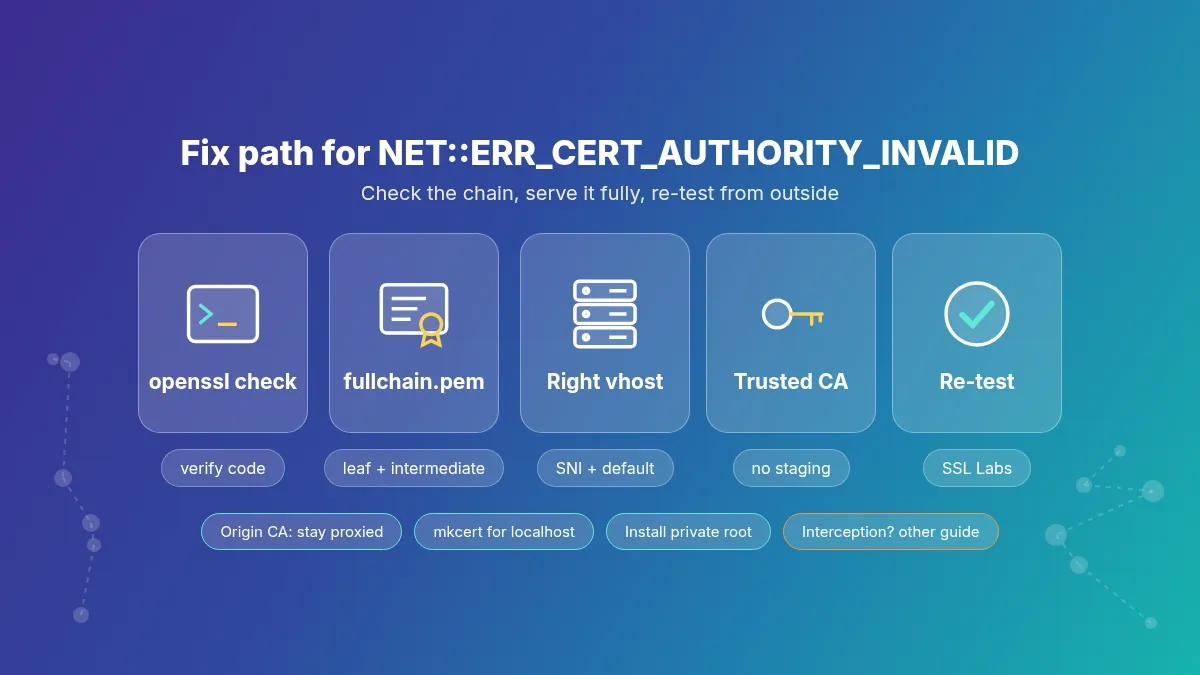
Step 1 — Serve the Full Chain
Certbot writes four files for each certificate. Use them like this:
cert.pem– leaf only. Do not use it alone for Nginx.chain.pem– intermediates only.fullchain.pem– leaf plus intermediates. Use this one.privkey.pem– the private key.
# Nginx
ssl_certificate     /etc/letsencrypt/live/example.com/fullchain.pem;
ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem;

# Apache 2.4.8+
SSLCertificateFile    /etc/letsencrypt/live/example.com/fullchain.pem
SSLCertificateKeyFile /etc/letsencrypt/live/example.com/privkey.pem
# Older Apache: SSLCertificateChainFile /path/intermediate.crt
With a commercial CA, build the chain yourself: leaf first, then the intermediate(s). The root is not needed. Then check that the leaf verifies against the intermediate:
cat example_com.crt intermediate.crt > fullchain.pem
openssl verify -untrusted intermediate.crt example_com.crt   # should print OK
In cPanel, Plesk and similar panels, paste the CA bundle into the Certificate Authority Bundle (CABUNDLE) field when installing the certificate. Wrong order breaks the chain even if every file is present.
Step 2 — Make Sure the Right Virtual Host Answers
List what the server actually loads, so you do not edit a file that is never used:
sudo nginx -T | grep -E "server_name|ssl_certificate"
sudo apachectl -S
Every hostname you serve, including www, needs a 443 server block with the right certificate. Otherwise the request lands on the default site and its self-signed certificate.
Step 3 — Replace Self-Signed, Default or Staging Certificates
Check what certbot has issued and whether any certificate came from staging:
sudo certbot certificates
sudo apt install certbot python3-certbot-nginx   # or python3-certbot-apache
sudo certbot --nginx -d example.com -d www.example.com --force-renewal
sudo certbot renew --dry-run
--force-renewal replaces a staging certificate with a production one; drop it for a first-time install. For Traefik, Caddy or a hosting panel, read the ACME log to see why issuance failed (blocked port 80, DNS not pointing at the server, rate limit), fix that, and let it reissue.
Step 4 — Cloudflare Origin CA: Keep It Behind the Proxy
An Origin CA certificate requires the DNS record to stay proxied (orange cloud) and works best with the SSL mode Full (strict). Create it in SSL/TLS → Origin Server, save the certificate and key on the server, and reference them:
# Nginx
ssl_certificate     /etc/ssl/cloudflare/origin.pem;
ssl_certificate_key /etc/ssl/cloudflare/origin.key;

# Apache
SSLCertificateFile    /etc/ssl/cloudflare/origin.pem
SSLCertificateKeyFile /etc/ssl/cloudflare/origin.key
sudo chmod 600 /etc/ssl/cloudflare/origin.key
sudo nginx -t && sudo systemctl reload nginxIf you need a record to stay DNS only (grey cloud), for example for a mail panel or an API, install a publicly trusted certificate on that hostname instead.
Step 5 — Reload and Re-Test From Outside
Run nginx -t or apachectl configtest, reload the service, purge the CDN cache if one sits in front, then repeat the openssl check and SSL Labs test. Also confirm the key matches the certificate:
openssl x509 -in fullchain.pem -noout -pubkey | openssl sha256
openssl pkey -in privkey.pem -pubout | openssl sha256   # both hashes must match
Local Development Certificates (mkcert)
For localhost or names like myapp.test, a self-signed certificate always triggers this error. mkcert creates a local CA, installs its root on your machine, and issues certificates signed by it:
mkcert -install
mkcert myapp.test localhost 127.0.0.1 ::1
# produces myapp.test+3.pem and myapp.test+3-key.pem
Point your dev server at those two files and restart Chrome. If the error persists on a phone or second computer, that device does not have the local root: find it with mkcert -CAROOT and install rootCA.pem there. Never share the rootCA-key.pem file and never use mkcert certificates on a public server.
Private and Internal CAs
If your organisation runs its own CA, the fix is to install its root certificate on each device, not to bypass the warning:
- Windows: open
certlm.msc, then Trusted Root Certification Authorities → Certificates → Import. In a domain, deploy it with Group Policy. - macOS: open Keychain Access, add the root to the System keychain and set it to Always Trust.
- Linux: copy it to
/usr/local/share/ca-certificates/as a.crtfile and runsudo update-ca-certificates. - Android: Settings → Security → Encryption & credentials → Install a certificate → CA certificate. Chrome accepts user-installed CAs, but many other apps do not.
Restart Chrome after installing. Only install roots from sources you control or trust; a root CA can vouch for any website.
Fixing NET::ERR_CERT_AUTHORITY_INVALID (Visitor Side)
Most of the time the site owner has to act. A few checks are still worth doing:
- Compare devices and networks. If the site works on mobile data but not at work, a proxy on that network is replacing the certificate. See SSL Certificate Not Trusted for interception and antivirus fixes.
- Check the issuer. If it names your antivirus, firewall or employer instead of a public CA, the certificate is being inspected on the way. An outdated inspection product may also sign with SHA-1, which Chrome reports as NET::ERR_CERT_WEAK_SIGNATURE_ALGORITHM. An outdated inspection product may also sign with SHA-1, which Chrome reports as NET::ERR_CERT_WEAK_SIGNATURE_ALGORITHM. An outdated inspection product may also sign with SHA-1, which Chrome reports as NET::ERR_CERT_WEAK_SIGNATURE_ALGORITHM.
- Public Wi-Fi. Captive portals intercept HTTPS until you sign in; open an
http://page to get the login screen. - Update the browser and system so the root store is current.
Do not click Proceed on sites where you log in or pay. On sites that use HSTS, Chrome hides that option completely.
Does NET::ERR_CERT_AUTHORITY_INVALID Affect SEO?
Yes, when it affects real visitors. Search engine crawlers generally expect a valid chain too, so persistent certificate errors can hurt crawling of HTTPS URLs. More directly, most visitors leave at a full-page security warning, which costs traffic and conversions. An incomplete chain is easy to miss because it may work on your own computer, so test from outside after every certificate change.
Prevention
- Always reference
fullchain.pemor the full CA bundle in server configuration. - Keep automatic renewal enabled and test it with
certbot renew --dry-run. - Run an external chain check, such as SSL Labs or
openssl s_client, after migrations and renewals. - Keep Cloudflare Origin CA certificates only on hostnames that stay proxied.
- Use mkcert or an internal CA for development and staging, and keep those certificates off public servers.
When to Contact Support
Ask your host or the certificate vendor for help when:
- openssl still reports code 20 or 21 after installing the CA bundle.
- You cannot edit the web server configuration or certificate files.
- The hosting panel keeps reinstalling a self-signed placeholder.
- Multi-domain or wildcard installation leaves some hostnames untrusted.
Send the openssl output, the SSL Labs report link and the exact hostnames affected.
Frequently Asked Questions
Chrome could not link the site certificate to a trusted root. The usual causes are a missing intermediate certificate, a self-signed or test certificate, or a private CA that is not installed on the device.
Your computer may have the missing intermediate cached or a private root installed. Other devices do not. Check the chain with openssl s_client or SSL Labs and serve the full chain.
Use fullchain.pem. It contains the leaf certificate plus the intermediates, while cert.pem holds only the leaf, which causes chain errors in Chrome and other clients.
Yes. Browsers do not trust Cloudflare Origin CA certificates. They only work while the DNS record is proxied through Cloudflare. A DNS-only hostname needs a publicly trusted certificate.
Use mkcert: run mkcert -install to add a local CA, issue a certificate for your dev hostnames, point the dev server at it and restart Chrome.
Only on a device or test site you control and recognise. On public sites, especially where you log in or pay, leave the page, because the connection cannot be verified.
Final Summary
NET::ERR_CERT_AUTHORITY_INVALID means Chrome cannot trace the certificate back to a trusted root. Check the chain with openssl s_client and SSL Labs, serve fullchain.pem, replace self-signed, default or staging certificates, keep Cloudflare Origin CA certificates behind the proxy, and install private or mkcert roots only on devices you manage.
Related SSL Errors
- SSL Certificate Not Trusted — Fix Guide
- SEC_ERROR_UNKNOWN_ISSUER (Firefox)
- ERR_CERT_COMMON_NAME_INVALID
- NET::ERR_CERT_DATE_INVALID
- Error 526 Invalid SSL Certificate
- SSL Handshake Failed — Causes and Solutions
- ERR_SSL_PROTOCOL_ERROR — Step-by-Step Fix
- Mixed Content Error — How to Fix HTTPS Issues
- Too Many Redirects After SSL — Fix Redirect Loop
Hi, I’m Alex — the person behind ErrorRescue.
I’ve been working with websites, servers, and hosting for over 8 years. Most of my experience comes from troubleshooting real problems on WordPress sites, VPS and shared hosting environments, and Cloudflare setups. I’ve dealt with everything from SSL certificate failures and DNS misconfigurations to 504 timeouts, memory exhaustion errors, and Cloudflare 5xx issues.
I started ErrorRescue because I got tired of seeing generic, outdated, or incomplete error guides. My goal is to write clear, practical fixes based on what actually works in production — not just theory. Every guide here is tested against common server setups (Apache, NGINX, Cloudflare, and popular WordPress stacks).
When I’m not fixing sites, I’m usually reviewing new hosting configurations or updating existing guides so they stay accurate.