SSL Handshake Failed (browser version) means your browser and the website’s server could not finish the TLS negotiation that starts every HTTPS connection. The secure channel never opens, so the page does not load. Browsers show it with different labels: Firefox often says SSL_ERROR_HANDSHAKE_FAILURE_ALERT or Secure Connection Failed; Chrome and Edge may show related messages such as ERR_SSL_PROTOCOL_ERROR or ERR_SSL_VERSION_OR_CIPHER_MISMATCH.
This guide focuses on the browser-side case: what you see on your device, how to isolate a local problem, and what to check if you manage the site. For Cloudflare’s origin SSL handshake page, see Error 525 SSL Handshake Failed.
Quick Fix
- Update your browser to the latest version and restart it.
- Check that your system date and time are correct (enable automatic time sync).
- Open the site in a private/incognito window with extensions disabled.
- Clear the SSL state (Windows) and browser cache, then retry.
- Temporarily disable antivirus HTTPS scanning / VPN / proxy.
- Try another browser or another network (for example mobile data).
- If you manage the site: confirm TLS 1.2/1.3, a valid certificate, and a full chain.
Most visitor-side failures clear after a browser update, a clock fix, or turning off HTTPS interception. Server-side failures need certificate or TLS configuration changes.
What SSL Handshake Failed Means
Before any page content loads over HTTPS, the client and server run a short TLS handshake. They must:
- Agree on a TLS protocol version (today that means TLS 1.2 or TLS 1.3).
- Present and validate a certificate for the hostname you typed.
- Pick a cipher suite both sides support.
- Exchange keys so the session can be encrypted.
If any step fails, the connection ends. You never reach HTTP status codes like 200 or 404 for that attempt. In plain language: the browser does not trust, or cannot speak the same security dialect as, the server.
Related visitor messages include Your Connection Is Not Private, SSL Certificate Not Trusted, and SSL Handshake Failed itself when the label is generic.
Why This Error Happens
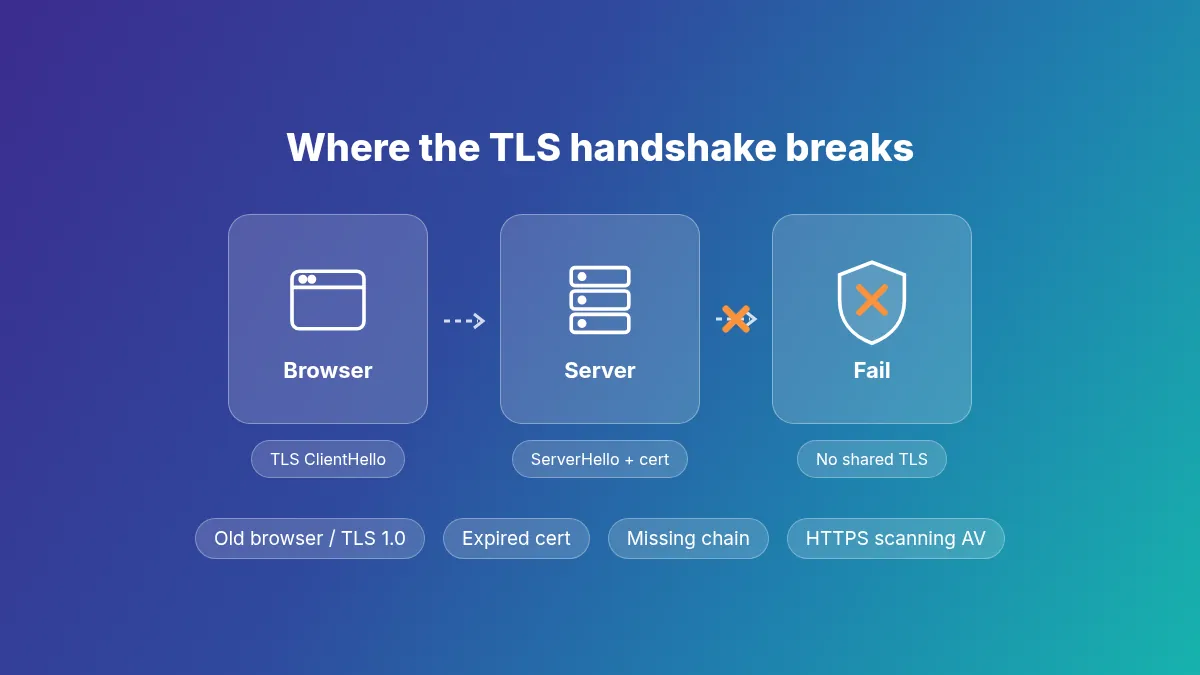
In practice the cause is usually one of these:
- Outdated browser or OS TLS stack that cannot speak TLS 1.2/1.3.
- Wrong system clock so a valid certificate looks expired or not-yet-valid.
- Expired, wrong-host, or incomplete certificate (missing intermediate certificates).
- Server disabled older protocols while a client still needs them, or the opposite: server only offers obsolete TLS.
- Overly strict cipher suites on the server or CDN.
- Security software intercepting HTTPS (antivirus SSL scanning, corporate proxy, some VPNs).
- Browser extensions that rewrite or block secure connections.
- CDN / reverse-proxy SSL mode mismatch (for example Cloudflare Full Strict with a bad origin cert).
Step-by-Step Fixes (Visitor Side)
1. Update the Browser and Restart
Install the latest Chrome, Edge, Firefox, or Safari build, then fully quit and reopen the browser. Old TLS stacks are a common cause of handshake failures on otherwise healthy sites.
2. Fix Date and Time
Enable automatic time zone and network time. A clock that is days off makes certificates fail validation and can abort the handshake.
3. Test in a Clean Profile
Open a private window with extensions disabled, or create a fresh browser profile. If the site loads there, an extension, theme, or corrupted profile data is involved.
4. Clear SSL State and Cache
On Windows: Control Panel → Internet Options → Content → Clear SSL State. Then clear the browser cache (or try Incognito). Cached redirects and stale TLS sessions can leave you stuck on a failed handshake.
5. Disable VPN, Proxy, and Antivirus HTTPS Scanning
Turn off the VPN and system proxy temporarily. In antivirus products, disable "HTTPS scanning", "SSL inspection", or "Safe Browsing HTTPS" for a test. These features insert their own certificate and often break handshakes when the local trust store is incomplete.
6. Try Another Network or Device
Switch to mobile data or another Wi-Fi network. If only one network fails, a captive portal, DNS filter, or firewall on that network is interfering.
Fixes If You Manage the Website
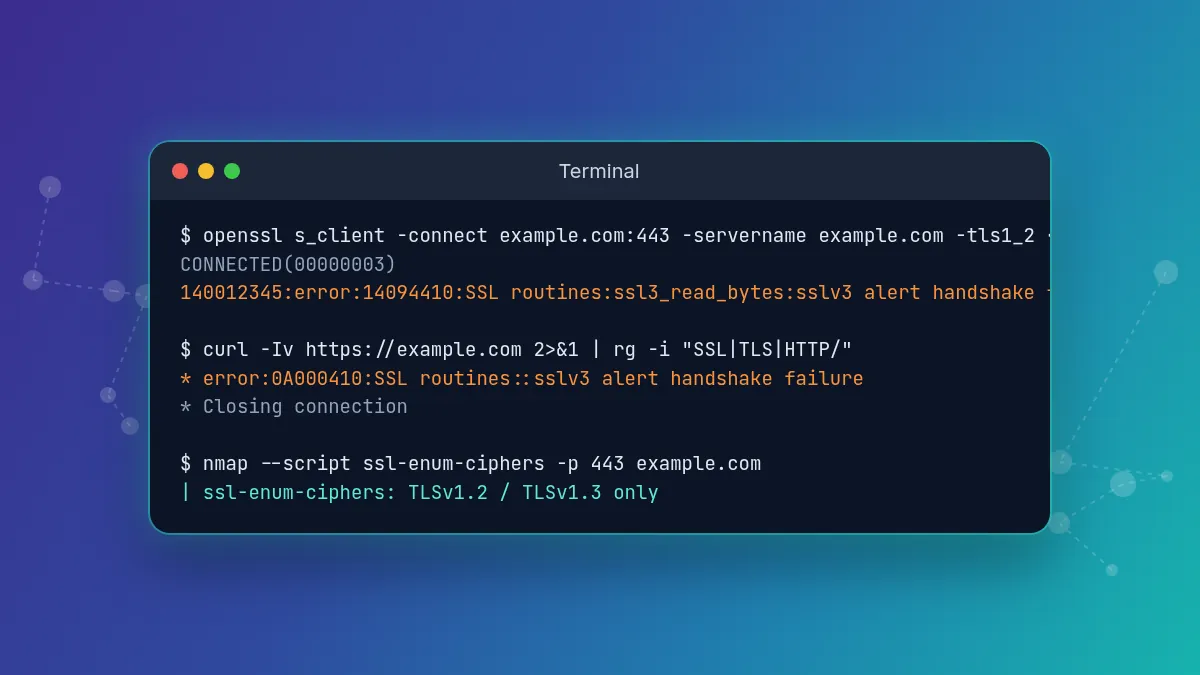
When many visitors on modern browsers report the error, treat it as a server or CDN issue.
1. Confirm Certificate Validity
- Not expired; covers the exact hostname (including
wwwvs apex). - Issued by a publicly trusted CA.
- Full chain installed (leaf + intermediates). Missing intermediates are a frequent handshake killer on mobile and some desktop stacks.
2. Enable TLS 1.2 and TLS 1.3
Disable SSL 3 / TLS 1.0 / TLS 1.1. Keep both 1.2 and 1.3 enabled for broad client support unless you have a documented reason not to.
3. Review Cipher Suites
Prefer modern Mozilla or cloud-provider intermediate profiles. Extremely locked-down cipher lists can exclude legitimate browsers.
4. Check CDN / Proxy SSL Mode
If you use Cloudflare or another proxy, align SSL/TLS mode with the origin certificate. Full (Strict) requires a valid cert on the origin. A broken origin often surfaces as visitor handshake errors or as Error 525.
5. Test the Origin Directly
Bypass the CDN briefly (hosts file or origin hostname) and test with:
openssl s_client -connect example.com:443 -servername example.com -tls1_2
curl -Iv https://example.com
Compare results with an SSL checker that reports chain and protocol support.
Advanced Troubleshooting
- Inspect server or CDN TLS logs for alert codes (handshake_failure, certificate_unknown).
- Check corporate firewalls that block certain TLS versions.
- Verify HSTS is not pinning users to a broken HTTPS setup after a migration.
- On Windows servers, confirm SChannel protocols; on NGINX/Apache, confirm
ssl_protocols/SSLProtocol.
Prevention Tips
- Turn on automatic certificate renewal and monitor expiry.
- Deploy the full chain every time you replace a cert.
- Test HTTPS after host migrations and CDN changes.
- Keep server packages and CDN SSL settings updated.
- Document a standard TLS 1.2+ cipher profile for all vhosts.
When to Contact Support
- The error appears on all modern browsers and networks.
- The certificate looks valid in a checker but visitors still fail.
- You cannot change TLS settings on a managed host or CDN.
Send the hostname, approximate time of failure, browser version, and any openssl s_client or CDN error codes you collected.
Related Errors
- Error 525 SSL Handshake Failed (Cloudflare origin)
- ERR_SSL_PROTOCOL_ERROR
- ERR_SSL_VERSION_OR_CIPHER_MISMATCH
- SSL Certificate Not Trusted
- Your Connection Is Not Private
- Mixed Content Error
- NET::ERR_CERT_AUTHORITY_INVALID
- Too Many Redirects After SSL
FAQ
No. An old browser, a wrong system clock, or antivirus HTTPS scanning can break it, but many cases are server-side: expired certificates, missing intermediates, or TLS/cipher settings.
Yes. HTTPS scanning features intercept TLS connections with a local certificate. If that certificate is not trusted by the browser, or the scanner mishandles the origin handshake, the connection fails.
That pattern usually points to something local on the desktop: extensions, VPN, antivirus HTTPS scanning, a wrong clock, or a corrupted SSL cache.
Use an SSL checker plus openssl s_client or curl -Iv. Confirm TLS 1.2/1.3, a hostname-matching certificate, and a complete chain.
If crawlers cannot complete HTTPS, they may fail to fetch the URL. Fixing TLS quickly limits crawl errors.
Visitor-side issues often clear in minutes after an update or clock fix. Server certificate renewal or chain repair is also typically quick once you have access.
Final Note
SSL Handshake Failed (browser version) is a compatibility or trust problem between client and server security settings. Start with browser updates, clock sync, and disabling HTTPS interception. If the failure is widespread, verify certificate chain and TLS 1.2/1.3 on the origin and CDN. Isolating "only me" versus "everyone" is the fastest way to pick the right fix path.
Hi, I’m Alex — the person behind ErrorRescue.
I’ve been working with websites, servers, and hosting for over 8 years. Most of my experience comes from troubleshooting real problems on WordPress sites, VPS and shared hosting environments, and Cloudflare setups. I’ve dealt with everything from SSL certificate failures and DNS misconfigurations to 504 timeouts, memory exhaustion errors, and Cloudflare 5xx issues.
I started ErrorRescue because I got tired of seeing generic, outdated, or incomplete error guides. My goal is to write clear, practical fixes based on what actually works in production — not just theory. Every guide here is tested against common server setups (Apache, NGINX, Cloudflare, and popular WordPress stacks).
When I’m not fixing sites, I’m usually reviewing new hosting configurations or updating existing guides so they stay accurate.