Last tested: November 7, 2026 · By Alex
Too many redirects after SSL appears when a browser is trapped in a redirect loop right after you install a certificate or force HTTPS. The request keeps bouncing between URLs and never reaches a final page. Chromium shows ERR_TOO_MANY_REDIRECTS; other browsers show similar redirect-loop errors.
This guide is SSL / HTTPS-migration specific: WordPress Site URL still on HTTP, Cloudflare Flexible SSL fighting origin redirects, duplicate HTTPS plugins, www vs apex rules stacked on top of HTTPS rules, and missing X-Forwarded-Proto behind a proxy. For cookie-only loops, plugin conflicts unrelated to SSL, and general debugging, use the broader guide ERR_TOO_MANY_REDIRECTS. Login-only loops belong in WordPress login redirect loop.
Redirect loops almost always mean two systems are trying to enforce opposite schemes or hostnames at the same time. Simplify to one HTTPS redirect authority and the loop usually stops within minutes.
Quick Fix
- Clear browser cookies and cache for the site (or test in a fresh private window).
- In WordPress Settings → General, set both WordPress Address and Site Address to
https://with the same host. - If wp-admin is unreachable, define
WP_HOMEandWP_SITEURLas HTTPS inwp-config.php. - Set CDN SSL mode to Full or Full (Strict) — avoid Flexible when the origin already redirects to HTTPS.
- Disable WordPress “force HTTPS” / redirect plugins while the server or CDN already forces HTTPS.
- Keep a single HTTP→HTTPS rule and a single www/apex rule; remove duplicates.
- Purge CDN and host caches after the change.
If the loop started the moment SSL was enabled, prioritize WordPress URL scheme and CDN SSL mode before hunting obscure rewrite rules.
What “Too Many Redirects After SSL” Means
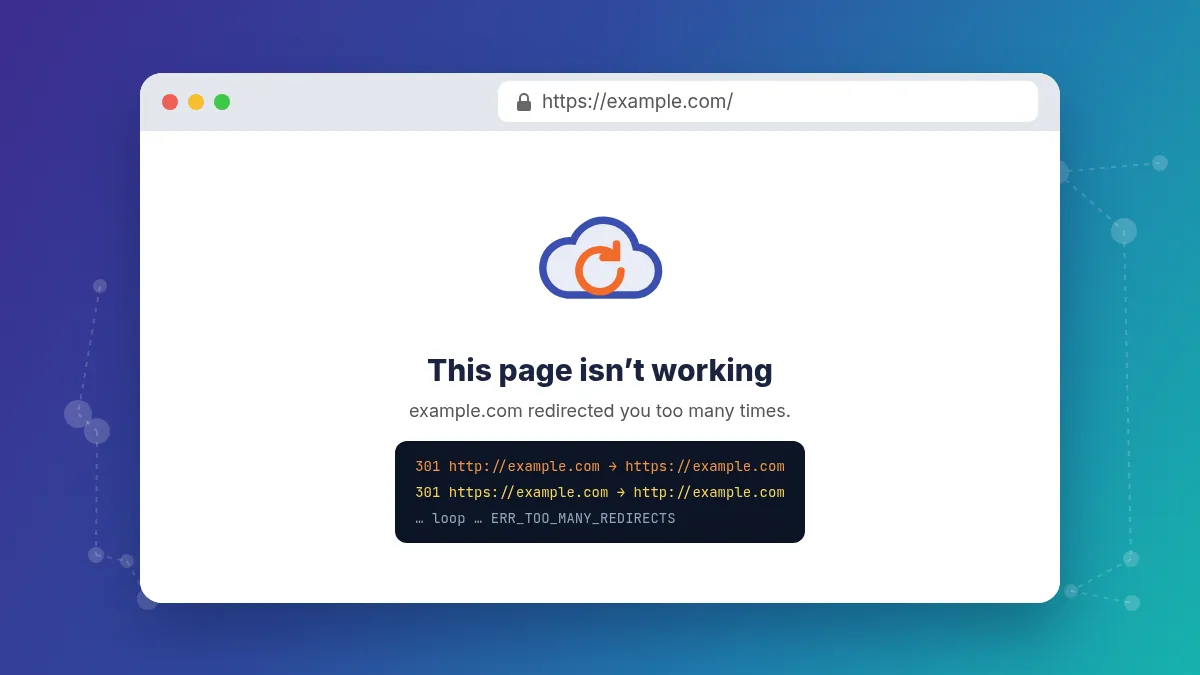
The browser follows a chain of HTTP 301/302 responses that never ends on a 200 page. After several hops it stops and reports a redirect loop. A classic SSL-migration loop looks like:
http://example.com→https://example.com(server or CDN)https://example.com→http://example.com(app still thinks site URL is HTTP)- repeat until the browser gives up
Variants include HTTPS apex ↔ HTTPS www fighting each other, or CDN Flexible SSL terminating TLS at the edge while the origin still issues an HTTPS redirect based on a cleartext connection. The symptom is the same: too many redirects after SSL.
Why Redirect Loops Happen After SSL Installation
1. Conflicting Redirect Rules
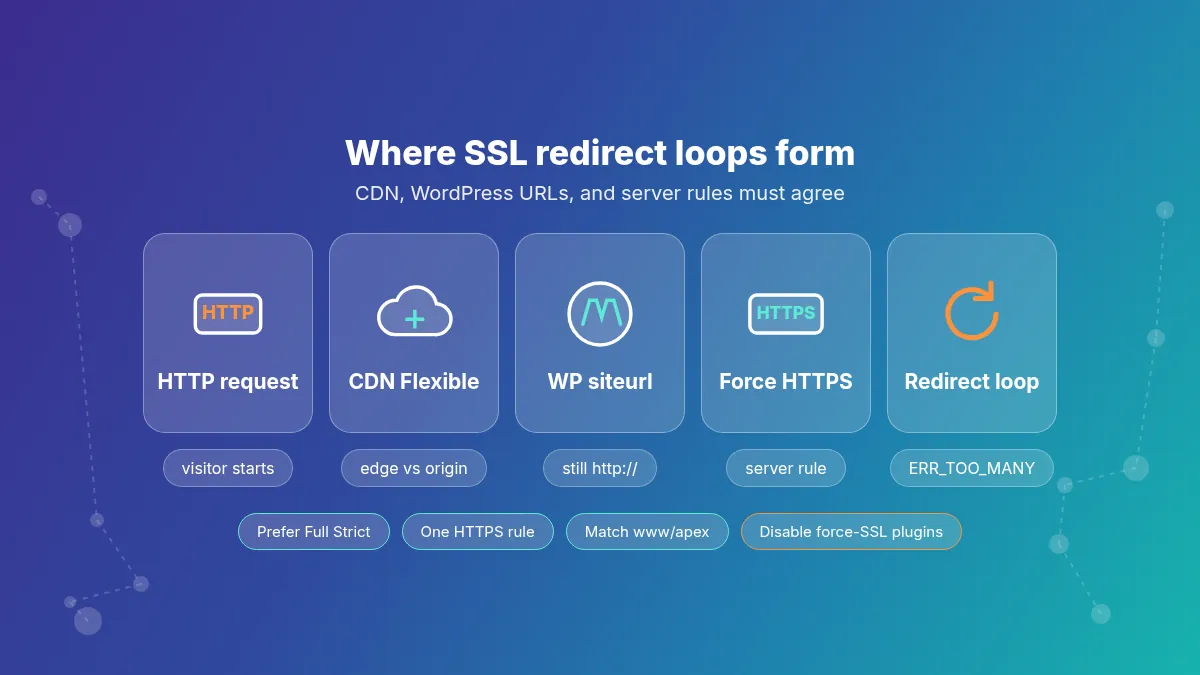
The server forces HTTPS while an application redirect (WordPress, a framework, or a plugin) sends the request back to HTTP. Two HTTPS redirect rules can also bounce between www and non-www forever if each rule rewrites the other’s host.
2. Incorrect WordPress URL Settings
If WordPress Address or Site Address still use http://, WordPress may generate HTTP canonical redirects even when the visitor arrived on HTTPS. That is the single most common WordPress cause right after flipping SSL on in the host panel.
3. CDN SSL Misconfiguration (Especially Flexible)
CDNs such as Cloudflare can enforce HTTPS independently from the origin. Flexible SSL encrypts browser↔CDN only; the origin sees HTTP. If the origin (or WordPress) then redirects HTTP to HTTPS, the CDN fetches HTTP again and the loop is born. Full or Full (Strict) with a valid origin certificate avoids that pattern.
4. Redirect / Force-SSL Plugins
Plugins that force HTTPS, add HSTS, or manage redirects often duplicate what the server and CDN already do. After migration, disable them until one layer owns HTTPS enforcement.
5. www vs Non-www Conflicts
Improper domain redirects combined with HTTPS rules produce endless hops: HTTP www → HTTPS www → HTTPS apex → HTTPS www … Pick one canonical host and one scheme, then redirect everything else once.
6. Missing Proxy Headers
Applications behind load balancers rely on X-Forwarded-Proto (or equivalent) to know the original request was HTTPS. Without it, the app believes the request is HTTP and redirects to HTTPS, while the proxy keeps talking HTTP to the origin.
How to Fix Too Many Redirects After SSL
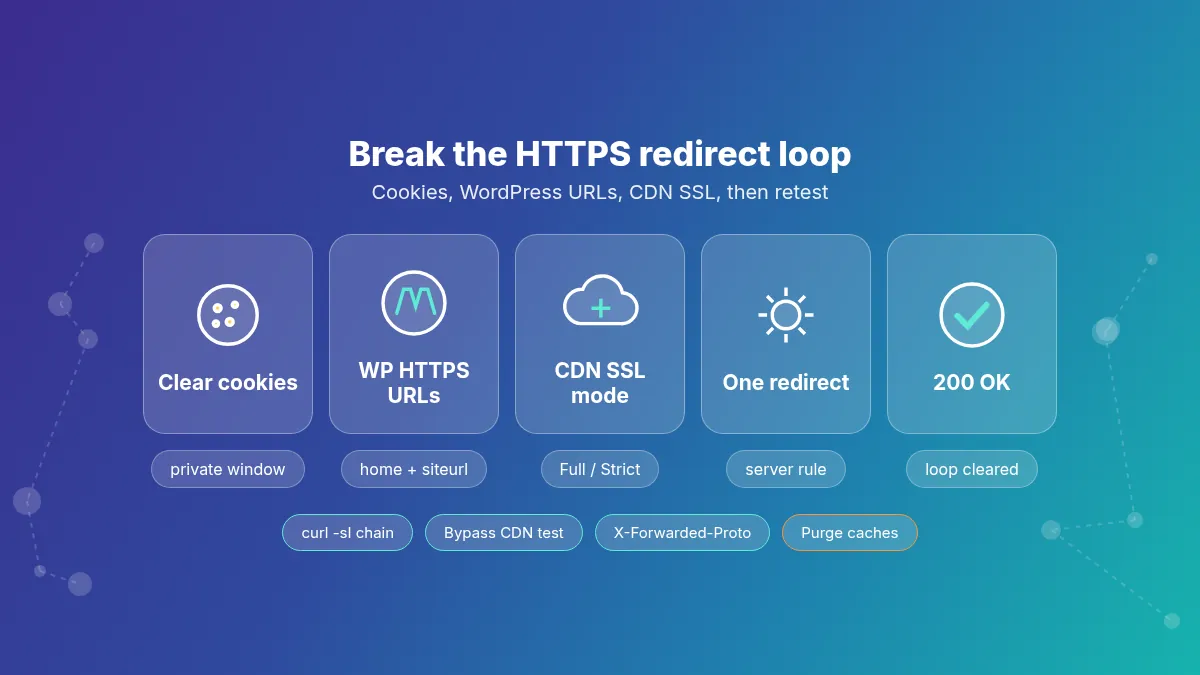
Step 1 — Clear Cookies and Test Clean
Clear cookies for the site and reload, or use a private window. Stale cookies rarely cause a brand-new SSL loop by themselves, but they confuse testing. For detailed browser-side steps that are not SSL-specific, see ERR_TOO_MANY_REDIRECTS.
Step 2 — Verify WordPress URLs
In WordPress go to Settings → General and ensure both:
- WordPress Address (URL) uses
https://and your canonical host - Site Address (URL) matches the same
https://host
If the admin area itself redirects forever, edit wp-config.php above the “stop editing” line:
define('WP_HOME', 'https://www.example.com');
define('WP_SITEURL', 'https://www.example.com');
// Optional while debugging behind a proxy:
if (isset($_SERVER['HTTP_X_FORWARDED_PROTO']) && $_SERVER['HTTP_X_FORWARDED_PROTO'] === 'https') {
    $_SERVER['HTTPS'] = 'on';
}
Match www vs non-www to the certificate SAN list. Wrong host + HTTPS force is how people bounce from a redirect loop into your connection is not private.
Step 3 — Inspect Server Redirect Rules
Check Apache or NGINX for duplicate HTTPS redirects. Keep a single rule.
# Apache — one HTTPS redirect is enough
RewriteEngine On
RewriteCond %{HTTPS} !=on
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]

# NGINX — example
if ($scheme = http) {
    return 301 https://$host$request_uri;
}
Remove older panel-generated rules that also force HTTPS. Confirm .htaccess does not fight NGINX when both are present on a hybrid stack.
Step 4 — Review CDN SSL Mode
If you use Cloudflare or another CDN:
- Origin should present a valid certificate (or at least a cert the CDN trusts in Full mode).
- Prefer Full or Full (Strict).
- Avoid Flexible when the origin or WordPress already redirects to HTTPS.
- Purge the CDN cache after changing SSL mode.
Flexible + origin HTTPS redirect is the textbook cause of too many redirects after SSL on Cloudflare WordPress sites.
Step 5 — Disable Redirect / Force HTTPS Plugins
Temporarily disable plugins that force SSL, add HTTPS redirects, or rewrite URLs sitewide. Use SFTP/File Manager to rename the plugin folder if wp-admin is unreachable. Server-level or CDN-level HTTPS should own the migration; the plugin can stay off afterward.
Step 6 — Fix Domain Redirect Rules
Ensure a consistent, one-hop path to the canonical URL:
http://example.com→https://example.com(or your chosen www host)http://www.example.com→ same HTTPS canonicalhttps://of the non-canonical host → HTTPS canonical once
Avoid chains that bounce three or four times. Search engines and browsers tolerate short chains; loops do not.
Step 7 — Confirm Mixed Content Is Separate
Once the loop is gone, open DevTools. Padlock warnings from HTTP images/scripts are mixed content, not redirect loops. Fix them after HTTPS loads cleanly.
Advanced Troubleshooting
Inspect the Redirect Chain
In DevTools → Network, reload and click the first document request. Read Status and Location headers for each hop. From a shell:
curl -sI -L --max-redirs 8 https://www.example.com/ | egrep -i 'HTTP/|location:'Stop when you see the hop that returns to a previous URL. That hop names the system still forcing the wrong scheme or host.
Test Without the CDN
Temporarily grey-cloud the DNS record or point a hosts-file entry at the origin IP. If the loop disappears off-CDN, fix SSL mode and cached redirect rules at the edge. If it remains, the origin or WordPress URLs are wrong.
Check Proxy Headers and HTTPS Detection
WordPress and many frameworks need to know the original scheme. Besides the X-Forwarded-Proto snippet above, confirm the load balancer actually sends the header and that you are not double-terminating TLS in a way that clears it. Some hosts prefer $_SERVER['HTTPS'] = 'on'; unconditionally when TLS always terminates upstream — use that only when every front-door request is HTTPS.
Database siteurl Still on HTTP
If the General settings screen is unreachable or keeps reverting, update the options directly:
# WP-CLI
wp option update home 'https://www.example.com'
wp option update siteurl 'https://www.example.com'

# Or SQL (backup first)
UPDATE wp_options SET option_value='https://www.example.com'
  WHERE option_name IN ('home','siteurl');
After updating, flush permalinks (Settings → Permalinks → Save) and purge caches. If posts return 404 instead of looping after the switch, see WordPress 404 error on posts. Serialized theme options that still embed http:// URLs are a mixed-content problem, not a redirect loop, unless a plugin reads them to build redirect targets.
Hosting Panel SSL Toggles
Many shared hosts offer a one-click Force HTTPS switch that writes its own rewrite rules. If you also added rules manually, delete one of the two. Likewise, turning SSL off and on again in the panel can reintroduce Flexible-style proxy behavior on bundled CDNs. After any panel toggle, re-check curl headers before changing WordPress again.
Elementor, WooCommerce, and Multisite Notes
Builders and commerce plugins cache absolute URLs. After fixing Site URL, re-save permalinks, clear builder CSS cache, and purge object cache. On multisite, each site’s siteurl / home rows in the database must use HTTPS for the domains you mapped.
HSTS Makes Bad Redirects Stickier
If you enabled HSTS before the redirect graph was clean, browsers will keep forcing HTTPS locally even while you debug. That is good once stable; during breakage see HSTS error for clearing site HSTS state while you repair the loop.
Does This Error Affect SEO?
Yes. Crawlers stop at the loop, so the URL becomes effectively unreachable. Users bounce immediately. Treat too many redirects after SSL as a production outage until curl shows a single clean hop to HTTP 200. Certificate failures are a different outage class (SSL certificate not trusted / SSL handshake failed); fix those first if TLS never completes.
Prevention Tips
- Use a single redirect strategy: one place forces HTTPS, one place forces the canonical host.
- Set WordPress URLs to HTTPS before or immediately when the certificate goes live.
- Prefer Full (Strict) CDN SSL once the origin cert is valid.
- Avoid stacking force-SSL plugins on top of server redirects.
- Test with curl and a private window before announcing the migration.
- Enable long-lived HSTS only after the redirect graph is stable.
- Keep staging on HTTPS so content never reintroduces HTTP siteurl values.
When to Contact Support
Contact your host or CDN if:
- You cannot edit server redirects or WordPress files.
- Behavior differs between CDN edges and origin.
- Managed SSL toggles keep rewriting your rules after you fix them.
- Load-balancer headers cannot be changed from your plan.
Send the curl -sI redirect trace, your canonical HTTPS URL, CDN SSL mode, and whether the loop happens with the CDN bypassed. For a general triage ladder across site errors, see how to fix website errors.
Frequently Asked Questions
Usually two redirect systems conflict: the server or CDN forces HTTPS while WordPress, a plugin, or Flexible SSL still pushes HTTP, or www and apex rules fight each other.
Sometimes cookies confuse tests, but a loop that starts right after SSL is usually WordPress URLs, CDN SSL mode, or duplicate HTTPS rules. Clear cookies, then fix those layers.
Yes. Flexible SSL often conflicts with origin or WordPress HTTPS redirects. Use Full or Full Strict with a valid origin certificate instead.
This article focuses on loops that start during HTTPS migration. The general guide covers cookies, plugins, and non-SSL redirect causes in more breadth.
It is not a certificate warning, but it makes the site unreachable for users and crawlers until you simplify the redirect chain.
Once you identify the conflicting hop with DevTools or curl, most WordPress and CDN fixes take minutes. Complex custom rewrite stacks can take longer.
Final Thoughts
Too many redirects after SSL means HTTPS was enabled in more than one place with conflicting rules. Set WordPress to HTTPS, pick Full/Strict CDN SSL, keep a single server redirect, disable duplicate force-SSL plugins, and verify the chain with curl.
Related reading: ERR_TOO_MANY_REDIRECTS for general loops, WordPress login redirect loop for wp-login only, mixed content once HTTPS loads, and your connection is not private when TLS trust fails instead of looping.
Related SSL Errors
- ERR_TOO_MANY_REDIRECTS
- WordPress Login Redirect Loop
- SSL Certificate Not Trusted
- Mixed Content Error
- Your Connection Is Not Private
- SSL Handshake Failed
- HSTS Error
- How to Fix Website Errors
Hi, I’m Alex — the person behind ErrorRescue.
I’ve been working with websites, servers, and hosting for over 8 years. Most of my experience comes from troubleshooting real problems on WordPress sites, VPS and shared hosting environments, and Cloudflare setups. I’ve dealt with everything from SSL certificate failures and DNS misconfigurations to 504 timeouts, memory exhaustion errors, and Cloudflare 5xx issues.
I started ErrorRescue because I got tired of seeing generic, outdated, or incomplete error guides. My goal is to write clear, practical fixes based on what actually works in production — not just theory. Every guide here is tested against common server setups (Apache, NGINX, Cloudflare, and popular WordPress stacks).
When I’m not fixing sites, I’m usually reviewing new hosting configurations or updating existing guides so they stay accurate.