403 Forbidden in WordPress means the web server understood the request but refuses to authorize it. Unlike a 404 Not Found, the resource usually exists. Something in file permissions, .htaccess, a security plugin, ModSecurity, or a CDN/WAF is blocking access.
The block can hit a single URL, /wp-admin, the REST API, uploads, or the whole site. This guide walks through the common WordPress causes in a safe order so you do not make the site worse while testing.
Quick Fix
- Hard-refresh the page and clear the browser cache (or try a private window).
- Confirm typical permissions: files
644, directories755,wp-config.phptighter (for example600). - Rename
.htaccessto.htaccess_old, then Settings → Permalinks → Save to regenerate it. - Temporarily disable security / firewall plugins (via wp-admin or by renaming the plugin folder over FTP/SFTP).
- Pause CDN/WAF rules (Cloudflare firewall, host ModSecurity) and whitelist your IP.
- Check the host error log for the exact rule that denied the request.
Most WordPress 403 errors come from permissions, a bad .htaccess rule, or a security product false positive.
What 403 Forbidden Means in WordPress
HTTP 403 is an intentional deny. The server (or a proxy in front of it) evaluated the request and rejected it. In WordPress environments the decision usually comes from:
- Filesystem permissions or ownership (user/group the PHP/web server runs as).
- Apache
.htaccessor NGINX rules. - Security plugins (Wordfence, iThemes, All In One WP Security, and similar).
- ModSecurity / host WAF / CDN firewall.
- Missing index file with directory listing disabled.
- Hotlink protection or bot/rate rules that also catch real users.
If the whole admin area is locked, you may need FTP/SFTP or the host file manager before you can reverse a plugin change. Related recovery guides: White Screen of Death, Critical Error on This Website, and WordPress Stuck in Maintenance Mode.
Main Causes of WordPress 403
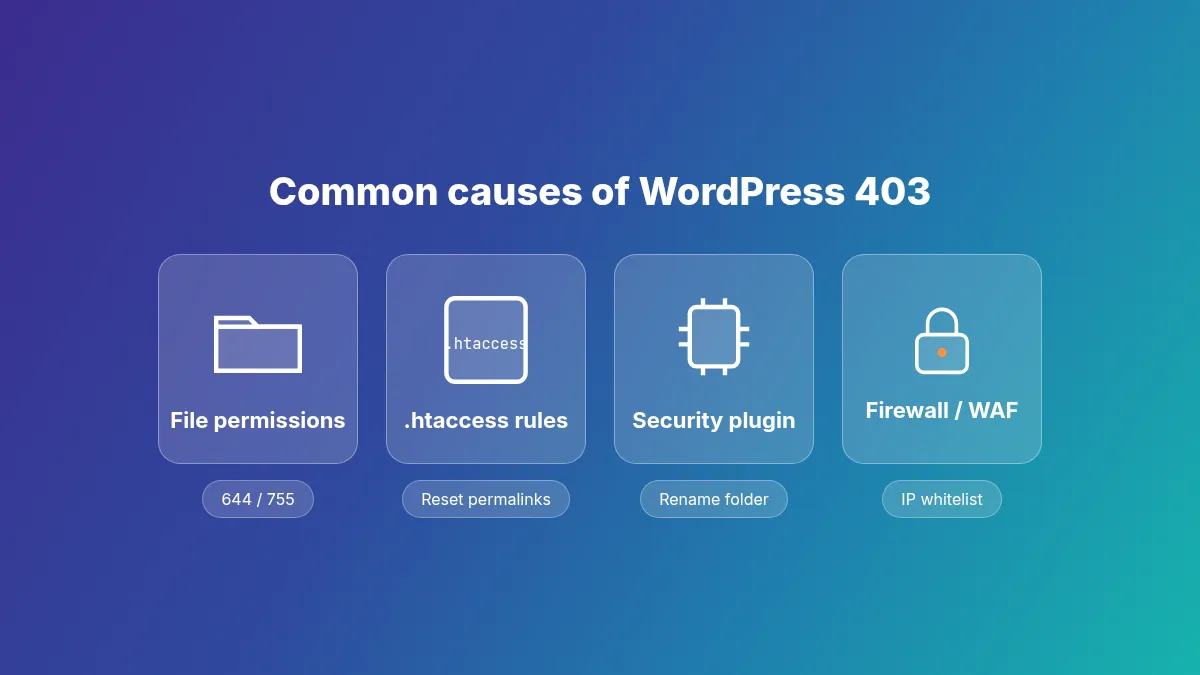
Incorrect File Permissions
Permissions that are too strict (or occasionally too open, if a host policy blocks insecure modes) prevent the web server from reading PHP or static files. Typical baseline:
- Directories:
755 - Files:
644 wp-config.php:600or640(host-dependent)
Corrupted or Strict .htaccess
A bad rewrite rule, an old security snippet, or a malformed Deny from all block can return 403 for admin, uploads, or every pretty permalink.
Security Plugin False Positives
Plugins may block countries, user agents, XML-RPC, rest routes, or "suspicious" query strings. After an update they sometimes lock out legitimate admins.
Firewall / ModSecurity / CDN
Host ModSecurity rules and CDN WAFs (Cloudflare, Sucuri, and others) can flag login, checkout, or plugin-install requests. The response still looks like a WordPress 403 even when WordPress itself never ran. If the page has the Cloudflare layout and a Ray ID, Cloudflare Error 1020 shows how to tell which Cloudflare feature blocked the request.
Missing Index / Directory Browsing Off
Requesting a directory without an index file while Indexes are disabled often yields 403 instead of a listing.
Step-by-Step Fixes
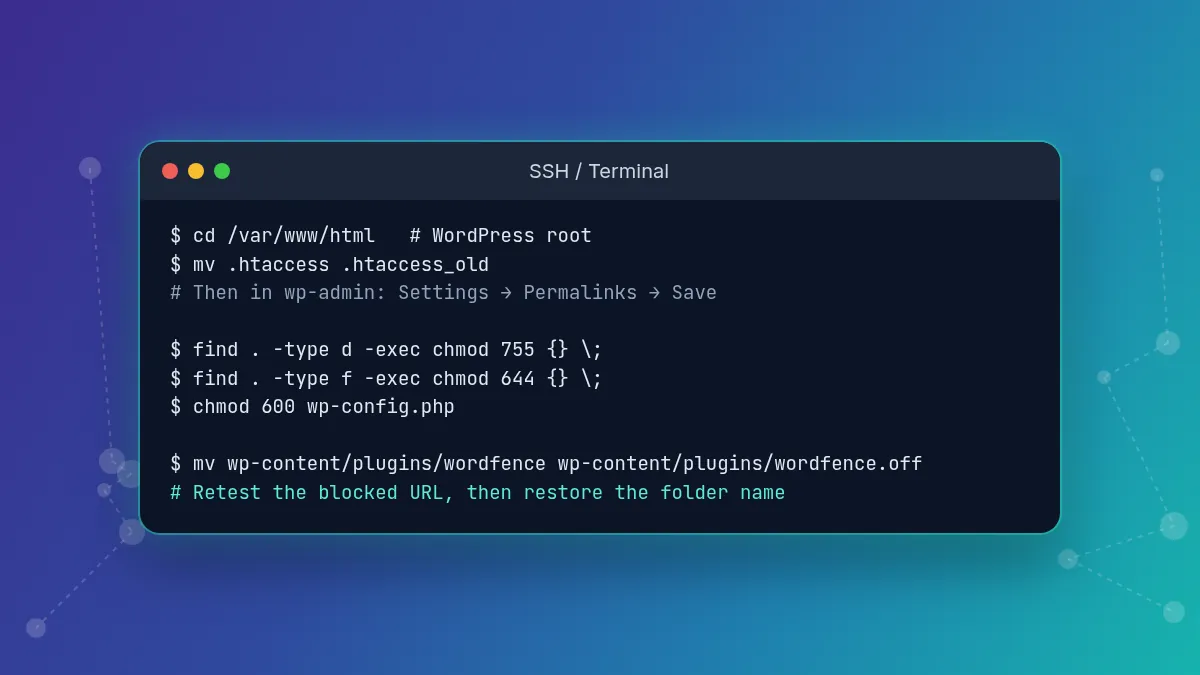
1. Clear Caches
Clear browser cache and any page/CDN cache. Retest with a private window so you are not staring at a cached 403.
2. Fix File Permissions
From SSH in the WordPress root (adjust the path for your host):
find . -type d -exec chmod 755 {} \;
find . -type f -exec chmod 644 {} \;
chmod 600 wp-config.php
Also confirm ownership matches what the host documents (often the account user, not root).
3. Reset .htaccess
- Connect with FTP/SFTP or the host file manager.
- In the WordPress root, rename
.htaccessto.htaccess_old. - If the site loads, open wp-admin → Settings → Permalinks → Save Changes to write a fresh file.
- Re-apply only the custom rules you still need, one block at a time.
On NGINX there is no .htaccess; check the site vhost and any include files your host provides.
4. Disable Security Plugins
If you can reach wp-admin, deactivate security and firewall plugins temporarily. If you cannot, rename the plugin folder:
wp-content/plugins/wordfence → wordfence.offRetest the blocked URL. If access returns, open the plugin settings, whitelist your IP, and reverse the folder rename.
5. Check CDN and Host Firewall
- Cloudflare: Security → Events; whitelist your IP; temporarily set under-attack / WAF to a softer mode for testing.
- Ask the host to review ModSecurity hits for your IP and URL around the failure time.
6. Read the Error Log
Look for access denied, ModSecurity, client denied by server configuration, or plugin-specific deny lines. The log usually names the rule faster than guessing.
Advanced Checks
- IP allow/deny lists in
.htaccess, NGINXallow/deny, or host panel IP blocker. - Hotlink protection blocking CSS/JS referrers and producing secondary 403s.
- Incorrect document root after a migration (web server pointing at a locked directory).
- REST API or
admin-ajax.phpblocked by a security plugin while the front page still loads.
Does 403 Affect SEO?
Yes. If Googlebot repeatedly receives 403 on important URLs, those URLs may drop out of the index. Short, accidental blocks rarely matter; multi-day blocks on canonical pages do. Fix the rule, then request recrawl for key URLs in Search Console if needed.
Prevention
- Keep to recommended WordPress permissions; avoid
777. - After installing a security plugin, whitelist your office/home IPs.
- Test firewall rule changes on staging when possible.
- Keep backups so you can restore a known-good
.htaccess. - Watch host security emails/logs after plugin or theme updates.
When to Contact Support
- You cannot identify the denying rule from logs.
- ModSecurity or host WAF settings are locked to the provider.
- The entire site returns 403 after a host-side change.
Provide the URL, timestamp, your IP, and any log lines you already found.
Related Guides
- 401 Unauthorized
- 404 Not Found
- White Screen of Death
- Critical Error on This Website
- WordPress Stuck in Maintenance Mode
- Error Uploading Image in WordPress
- WordPress Login Redirect Loop
FAQ
The server (or a firewall in front of it) received the request but refused access. The page often exists; permission or a security rule is blocking it.
Yes. Security and WAF plugins commonly block admin paths, REST routes, or requests they treat as suspicious.
Yes. Directories and files that the web server cannot read frequently produce 403 responses.
Usually not. Most cases come from server configuration, plugins, or firewall rules. A banned IP is still a server-side decision.
Rename the existing file, confirm the site responds, then Save Permalinks in wp-admin to regenerate a default WordPress .htaccess.
Once you find the denying rule, many 403s clear within minutes. Finding the rule in logs is the slow part.
Summary
403 Forbidden on WordPress is an access deny from permissions, .htaccess/NGINX rules, security plugins, or a host/CDN firewall. Work from cache and permissions to .htaccess reset, then plugin and WAF checks, and use the error log to confirm which layer said no. After access returns, re-enable security tools carefully with your IP whitelisted.
Hi, I’m Alex — the person behind ErrorRescue.
I’ve been working with websites, servers, and hosting for over 8 years. Most of my experience comes from troubleshooting real problems on WordPress sites, VPS and shared hosting environments, and Cloudflare setups. I’ve dealt with everything from SSL certificate failures and DNS misconfigurations to 504 timeouts, memory exhaustion errors, and Cloudflare 5xx issues.
I started ErrorRescue because I got tired of seeing generic, outdated, or incomplete error guides. My goal is to write clear, practical fixes based on what actually works in production — not just theory. Every guide here is tested against common server setups (Apache, NGINX, Cloudflare, and popular WordPress stacks).
When I’m not fixing sites, I’m usually reviewing new hosting configurations or updating existing guides so they stay accurate.